DATA LEAK ACTIVE TESTING
Data theft: one way out is all it takes.
We run controlled campaigns with synthetic payloads, through your real egress controls, and report what was attempted, transmitted and collected, scenario by scenario.
- Synthetic test payloads only
- Flexible deployment
- Test destinations defined with you during scoping
THE REALITY
Your controls are in place. Their effectiveness is assumed.
DLP, EDR, proxy, firewall: validated at installation, rarely put to the test since. Policies drift with every change. A typical case: DNS, FTP and paste sites blocked while other paths are left wide open. The posture is uneven.
01
Do you know all your exit vectors?
Few teams have an up-to-date map of the channels left open in their environment.
02
Has your filtering ever actually blocked anything?
When did you last check? Thresholds and drift are rarely measured.
THE ENFORCIS PLATFORM
Test your exit paths before attackers do.
One tactic, covered in depth: exfiltration. Keep your DLP, your EDR and your pentests. We show you, on the scenarios actually tested, what was attempted, transmitted and collected on each exit path, to be read against your logs.
The 8 channels tested, what is not covered and how data is handled →
- 01
TestWith synthetic payloads, we run controlled campaigns on the configured paths.
- 02
ObserveFor each scenario tested: what was expected, attempted, transmitted, collected and persisted, with its execution status and a dated result. The blocked or detected reading comes from confronting those results with your DLP or SOC logs.
- 03
FixToday, findings are analysed and prioritised with our team. Upcoming versions will bring contextual, prioritised recommendations, validated by retest.
- 04
ReplayToday, each campaign can be replayed on request. Upcoming versions will let you schedule periodic replays, or replays triggered by a change.
WHAT WE TEST
Synthetic data, very real exit paths.
Workstations
The agent (signed Windows binary) runs on a real machine in your estate: what it gets out on a tested scenario, a user or an attacker could get out the same way. Other systems: ask us.
Corporate network
HTTPS, HTTP, DNS, FTP, ICMP: the outbound channels left open, and the volume that triggers your filtering.
Cloud and applications
Google Drive, GitHub Gist, DPaste (paste site): the cloud services through which data leaves the company.
Synthetic by design
Test payloads are synthetic; no real customer business data is used as a campaign payload. Agents in your environment, orchestration as an Enforcis SaaS; on-premises deployment possible, subject to assessment, for critical environments. Hybrid topologies (your private cloud) are under study. Test destinations are defined with you when scoping the POC or the pilot. Technical metadata (agent state, host and network information, campaign results) reaches the orchestration; the exact list is in the deployment documentation.
COMPLIANCE
Add what actually gets out to your audit files.
Every campaign is timestamped and repeatable: you add the date, the channel and the result to your audit file.
INTERNATIONAL AND EUROPE
ISO/IEC 27001:2022
ANNEX A · 8.12 AND 8.16
Data leakage prevention and monitoring activities.
NIS2
ARTICLE 21
Assessing the effectiveness of risk-management measures.
DORA
FINANCIAL ENTITIES
Digital operational resilience testing, alongside threat-led testing.
UNITED STATES
NIST CSF 2.0
PR.DS AND ID.IM
Data security outcomes, and improvements identified from security tests and exercises.
SEC and NYDFS
FORM 10-K ITEM 1C · 23 NYCRR 500
Factual material for your cybersecurity disclosures and your annual NYDFS certification.
HIPAA Security Rule
45 CFR 164.308(a)(8) AND 164.312(e)
Periodic technical evaluation of your safeguards, and transmission security for ePHI.
WHERE TO START
Where does your data get out? Three ways to start.
OPEN ACCESS
The DLP Proof Kit
7 templates to fill in to show, on scenarios that have actually been tested, what your egress controls really stop, and what they let through, beyond their configuration alone. A 10-page PDF.
GUIDED
A 30-minute guided demo
From a standard browser, on pre-built result sets: how version 1.0 works and its interface, a campaign across the 8 channels covered, the report and the report detail. Nothing to install, no contact with your environment.
SYNTHETIC DATA, REAL EGRESS CONTROLS
A POC on a standard scenario
With synthetic data, from a representative machine placed in your network: the test traffic crosses your real egress controls, with no real business data. Fast, usually free. Then, if you wish, a paid pilot on a limited production scope, with a report and findings analysed with our team.
OUR ARTICLES
Testing exfiltration, channel by channel.
THE GUIDEData exfiltration testing: definition, method and what is at stakeWhat the test covers, what it does not, and how to run one in 5 steps.Read the article →CHECKLISTHow to test your DLP: channel-by-channel checklist and test planA plan you can put to work next week to find out what your DLP really stops, on the scenarios actually tested.Read the article →FRAMEWORKMITRE ATT&CK Exfiltration (TA0010): the defender’s guideExfiltration techniques, how they map to your controls and how to test them.Read the article →
FREQUENTLY ASKED QUESTIONS
What runs on your side, and how to start.
Is it risky to test in production?
Our campaigns use synthetic payloads only: no real customer business data is used as a campaign payload, which is why they can run in production. The agent runs on a representative Windows machine in your estate (signed binary); other systems: ask us. You stay in control of the scope: together we define the segments tested, the agents and when each campaign runs. To get started, the POC runs a standard scenario with synthetic data from a representative machine placed in your network: the test traffic crosses your real egress controls, with no real business data.
What gets installed in our environment?
A Windows software agent (signed binary) on a representative machine: one execution point per exit path or egress policy you want to test. One agent per VLAN or subnet may be needed when routing or policies differ. An orchestrator drives the agents and consolidates the results, and a console lets you launch and monitor campaigns. Agents in your environment, orchestration as an Enforcis SaaS; on-premises deployment possible, subject to assessment, for critical environments. Hybrid topologies (your private cloud) are under study. Upcoming versions will bring SIEM integrations.
How do we get started?
With a 30-minute guided demo, on pre-built result sets, of how version 1.0 works and of its interface: a campaign across the 8 channels covered, the report and the report detail. Nothing to install, no contact with your environment. Next comes the POC: a standard scenario, with synthetic data, from a representative machine placed in your network. The test traffic crosses your real egress controls, with no real business data. Fast, usually free. Then a paid production pilot on a limited scope, with synthetic payloads only: dated results, a report you can read in detail, findings analysed with our team, and the campaign replayed on request to check the fixes. Together we set the scope, the duration and the launch date. After that, campaigns can be relaunched as needed. Upcoming versions will let you schedule periodic replays, or replays triggered by a change, depending on how critical the scope is and how fresh the results need to be.
What does the deliverable look like?
Today, each campaign gives dated, traceable results within the scope actually tested: for each scenario, what was expected, attempted, transmitted, collected and persisted, the execution status (complete, partial, missing) and the observed transmission rate (transmitted / expected, in files and in volume), in a report you can read in detail. A transmission that does not complete is not, by itself, proof that a control worked: the reading against your DLP or SOC logs is done during the analysis. Tests are already mapped to MITRE ATT&CK in the console. Upcoming versions will bring multi-level reporting (leadership, CISO, operations), MITRE D3FEND where the correspondence is established, and SIEM integrations. They will also bring contextual, prioritised recommendations, validated by retest.
DLP PROOF KIT · PDF, 10 PAGES
From test trace to board report
7 templates to fill in to show, on scenarios that have actually been tested, what your egress controls really stop, and what they let through, beyond their configuration alone.
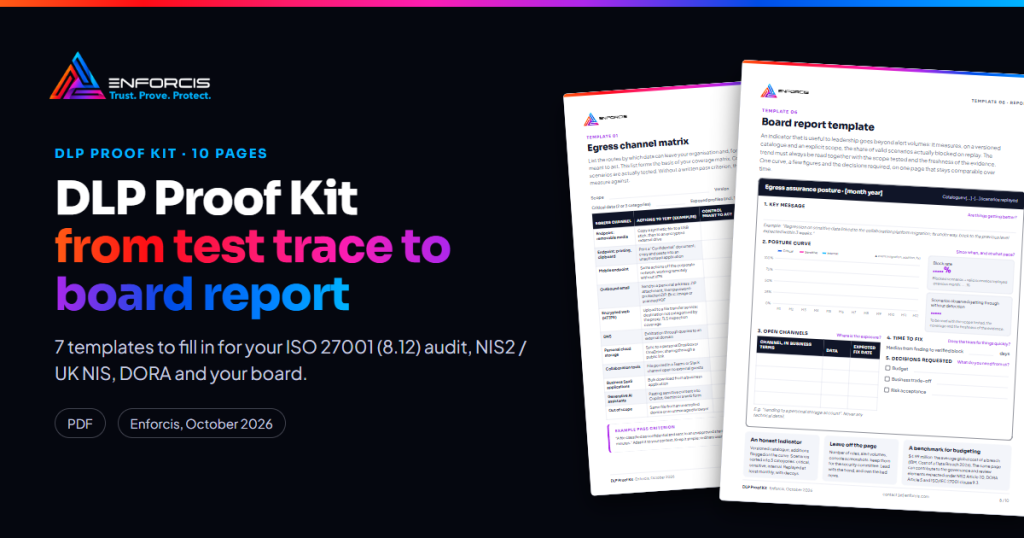
Read 3 pages of the kit before downloading →
Exit channel matrix, scenario sheet, campaign register and gap register
Microsoft Purview™ validation matrix across 5 locations
Board page template and ISO 27001, NIS2, DORA, GDPR mapping
Get the DLP Proof Kit by email
30-MINUTE DEMO
What actually leaves your network?
Discover, in a guided demo on pre-built result sets, how version 1.0 represents and reports a campaign across the 8 channels covered, scenario by scenario: report, report detail and MITRE ATT&CK mapping. Get ahead, and act before attackers do.
Reply within 24 hours
A product expert on the call with you
Nothing to install for this demonstration
WHO WE ARE
An international team focused on exfiltration.
It all started in 2021 at Holiseum, with the ransomware blank-fire exercise (Tir à Blanc de Ransomware), which won awards in 2022 (first prize at Cybernight, first prize at the Cas d’Or de la Cybersécurité). After 40 runs of that exercise and a white paper in 2023, we founded Enforcis in 2025 to focus on a single subject: data leaving the organisation.
Faiz Djellouli
CEO AND FOUNDER
20+ years in engineering and cybersecurity
Pierre Dewez
CTO
27+ years in cybersecurity, audit and certification
Christophe Leleu
LEAD DEVELOPER
20+ years in deep tech development